Modern application security requires multiple layers working together. By combining WAF, DDoS protection, bot management, API security, Zero Trust access, and edge enforcement, organizations can better protect applications, users, and data against evolving threats while maintaining performance and availability.
Cloudflare provides the technical building blocks for a strong application security architecture, but effective security depends on how those capabilities are designed, integrated, and managed. WinCap helps organizations assess their environment, implement the right controls, and build a security approach aligned with business and operational requirements.
Modern applications are not protected by a single product or perimeter. They depend on users, APIs, cloud services, identity providers and third-party systems—each creating a decision about what should be allowed, challenged or blocked.
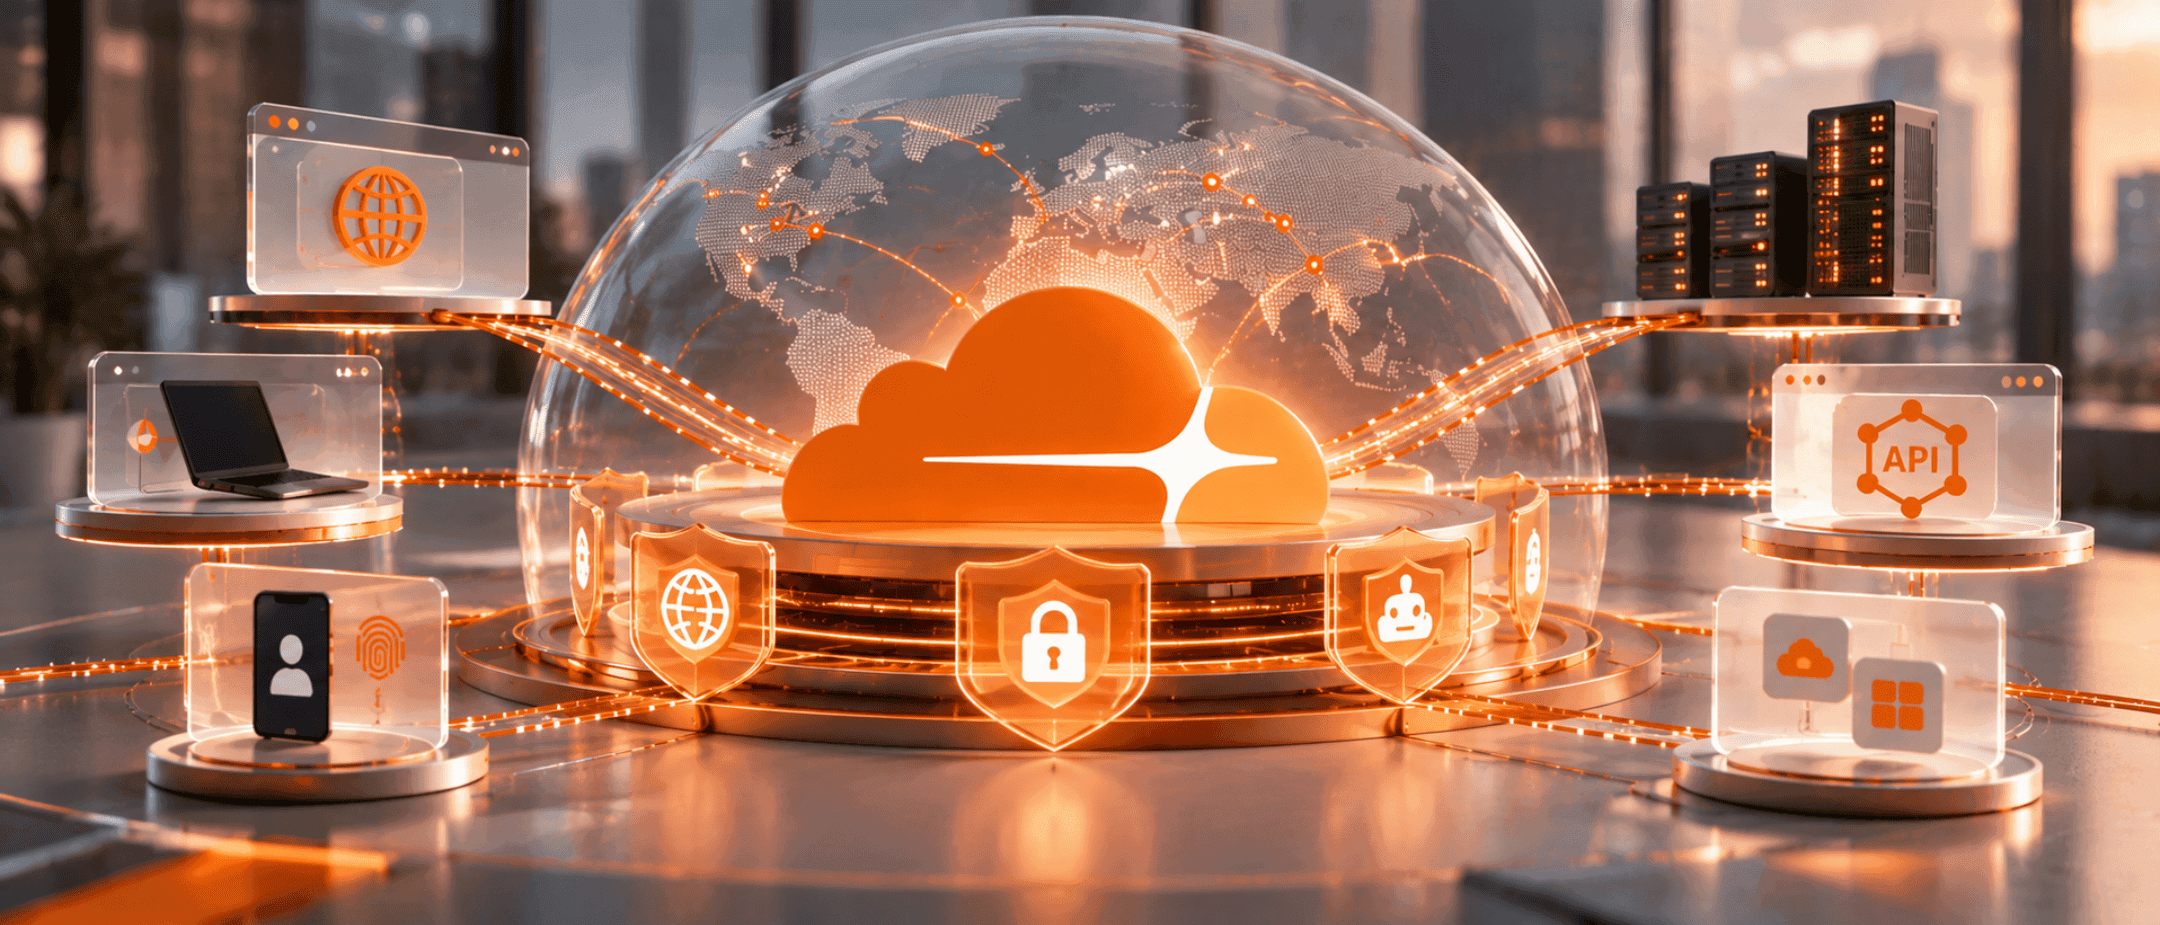
Cloudflare brings several of those decisions together across its security platform. The result is a layered model that protects applications and APIs, controls access and reduces exposure before unwanted traffic reaches critical services.
The value comes not from deploying isolated tools, but from designing them to work as one security architecture.
1. Web Application Firewall: Filter Threats Before They Reach the Application
Cloudflare WAF inspects incoming web and API requests and applies managed and custom rules to identify unwanted traffic. Placing this control in front of applications helps reduce exposure to common attack patterns and gives security teams a consistent enforcement point.
A WAF is most effective when rules reflect the application’s behaviour and risk profile rather than being treated as a set-and-forget control.
2. DDoS Protection: Preserve Availability Under Attack
DDoS attacks attempt to exhaust applications, websites or networks with disruptive traffic. Cloudflare helps absorb and mitigate that traffic across its network so legitimate users can continue to reach services.
This makes availability part of application security: an application that cannot be reached cannot support customers, employees or operations.
3. Bot Management: Distinguish Users from Automation
Automated traffic can support legitimate activity, but it can also enable scraping, credential attacks, inventory abuse and other unwanted behaviour. Cloudflare’s bot capabilities help identify automation and apply an appropriate response—allow, monitor, challenge or block.
The objective is not to block every bot. It is to make better decisions about which automated interactions the application should trust.
4. Zero Trust Access: Control Access at the Application
Cloudflare One supports identity-first access to applications and resources. Policies can evaluate factors such as user identity, device context and permissions instead of granting broad trust based on network location.
This reduces dependence on legacy network access models and allows organisations to apply controls closer to the resource a person is trying to use.
5. API Security: Protect the Interfaces Behind Modern Applications
APIs often expose sensitive data and business functions, yet organisations may not have a complete inventory of them. Cloudflare supports API discovery, schema validation, authentication controls, rate limiting and protection against abusive traffic.
Effective API security begins with visibility: teams need to know which APIs exist, who uses them, what they expose and whether their behaviour matches expectations.
6. Security at the Edge: Apply Controls Earlier
Cloudflare applies security controls across its global network, closer to where traffic enters. This can help organisations block or challenge unwanted requests before they reach origin infrastructure and apply consistent policy across distributed applications.
Edge enforcement does not eliminate the need for secure origins. It adds another defensive layer and reduces the amount of hostile traffic those origins must process.
How the Layers Work Together
These capabilities address different questions within the same request:
- Is the traffic malicious?
- Is it part of a denial-of-service attempt?
- Is the requester a person or an automated system?
- Is the identity allowed to access this application?
- Is the API request valid and expected?
- Can the request be stopped before it reaches the origin?
When policies and telemetry are coordinated, the architecture becomes more than a collection of controls. It becomes a consistent way to evaluate traffic, identity and application behaviour.
Turning Cloudflare Capabilities into a Practical Architecture
Technology alone does not define which applications are critical, which identities should have access or which policies fit the business. Those decisions require an understanding of the existing environment.
This is where WinCap comes in.
WinCap helps organisations assess applications, APIs, identity systems, traffic flows and current controls before designing a Cloudflare architecture. That work can include prioritising exposed services, strengthening application protection, securing APIs and replacing broad network access with Zero Trust policies.
A practical implementation can follow four stages:
- Discover: map applications, APIs, users, data flows and dependencies.
- Prioritise: identify critical services, exposed interfaces and high-risk access paths.
- Design and deploy: select the appropriate WAF, DDoS, bot, API and Zero Trust controls.
- Optimise: review telemetry, tune policies and adapt protection as applications change.
Use the right controls for the environment you actually have; not the environment you wish you had.
Build Security Around the Application
Application security is most effective when traffic protection, API controls and identity decisions reinforce one another. Cloudflare provides the technical layers; WinCap helps align them with business requirements and the realities of the existing environment.
Ready to turn Cloudflare capabilities into a coherent application security architecture?
Design Your Cloudflare Security Architecture with WinCap
Frequently Asked Questions About Cloudflare Application Security
1. What does Cloudflare protect in an application security architecture?
Cloudflare can apply controls across web applications, APIs, automated traffic, availability and user access. The appropriate combination depends on the application, its exposure and the organisation’s risk priorities.
2. Is a WAF enough to secure a modern application?
No. A WAF is an important layer, but modern application risk can also involve APIs, identities, bots, DDoS attacks and configuration weaknesses. A layered architecture addresses these risks together.
3. How does Zero Trust complement application security?
Zero Trust evaluates access according to identity, device context, permissions and policy. It helps ensure that reaching an application does not automatically mean a user or device should be trusted.
4. Why is API discovery important?
Organisations cannot consistently protect interfaces they do not know exist. Discovery helps identify active APIs so teams can review exposure, authentication, expected behaviour and data access.
5. What role does WinCap play?
WinCap helps assess the current environment, translate business and security requirements into an architecture, implement appropriate Cloudflare controls and optimise them over time.